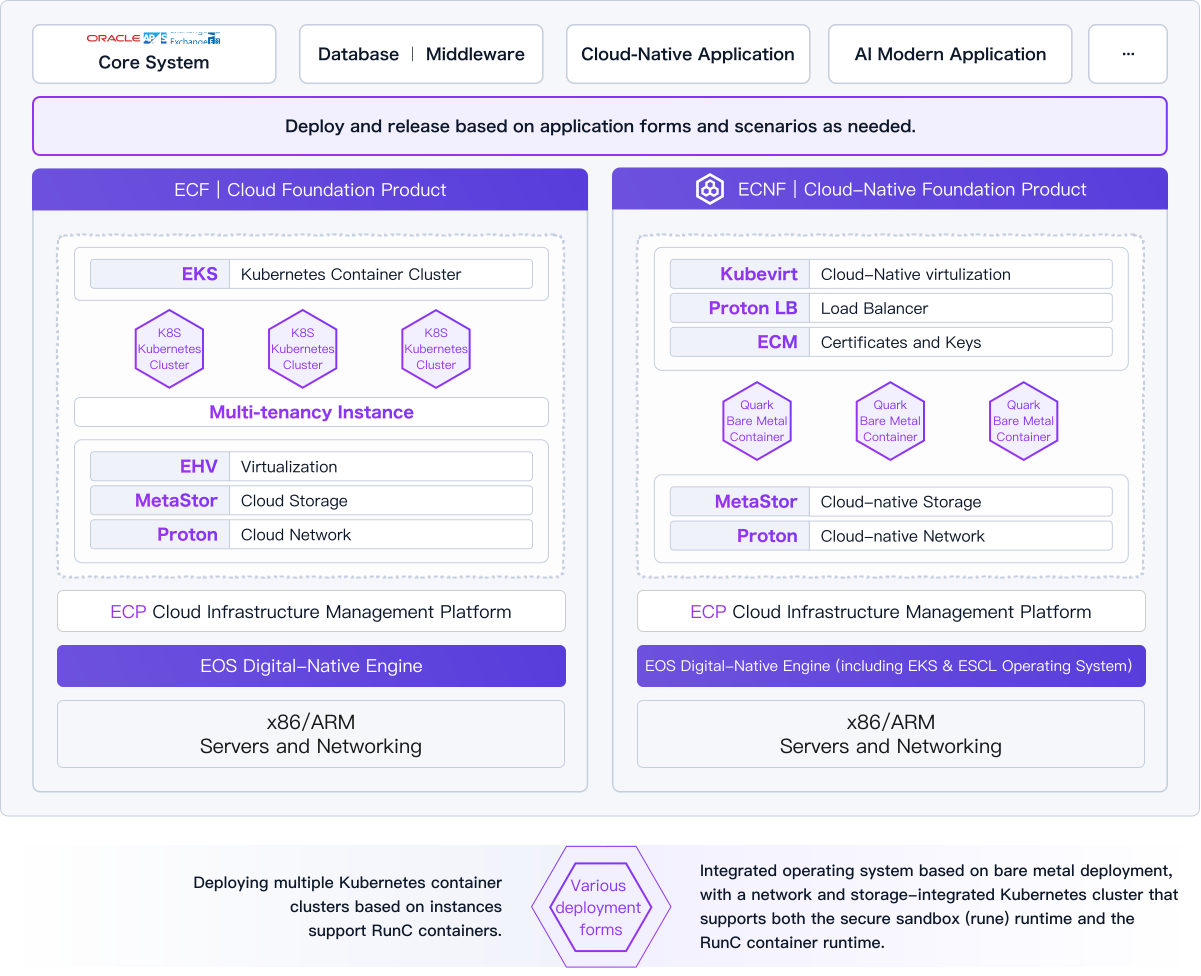
We provide you with
ECNF Cloud-Native Foundation Product
A Kubernetes, storage, and networking integration product designed for multiple container runtimes, used to build infrastructure for hosting modern applications
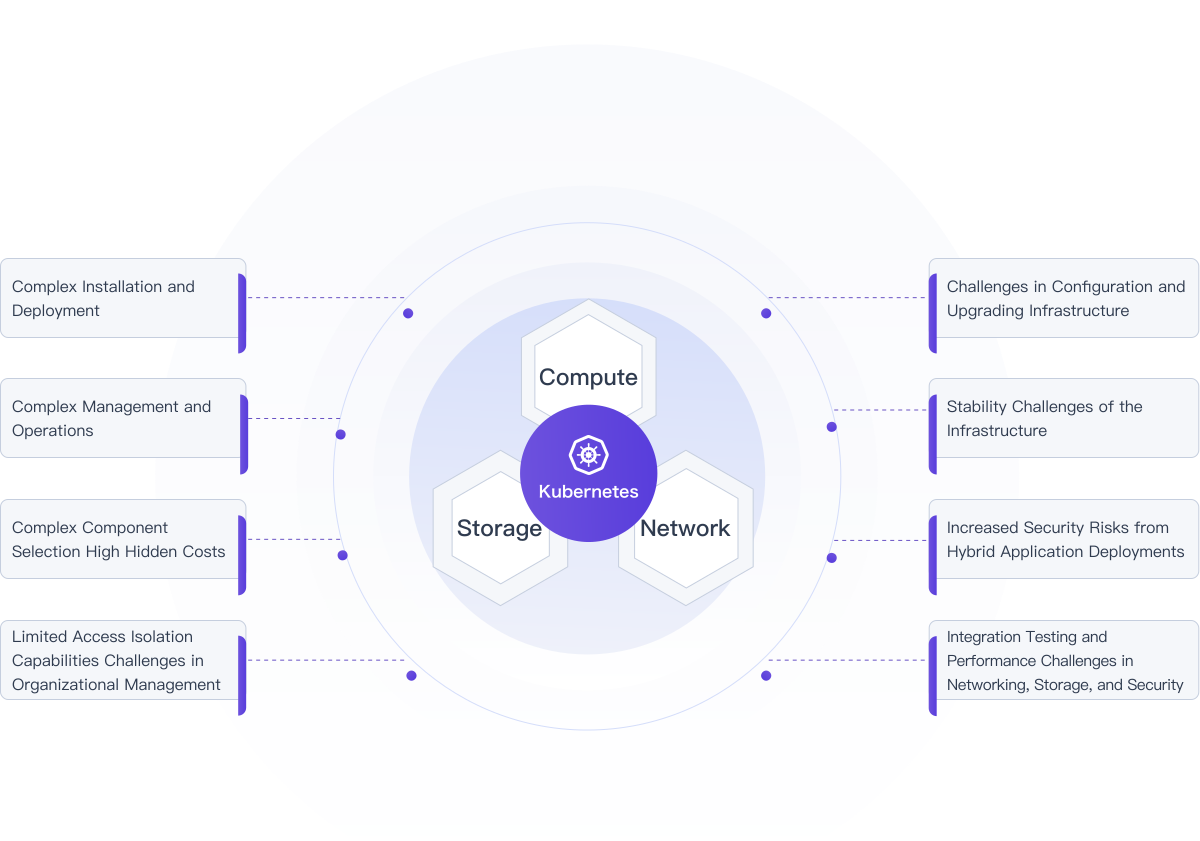
Challenges in Building Kubernetes-Centric Integrated Infrastructure for Compute, Storage, and Networking
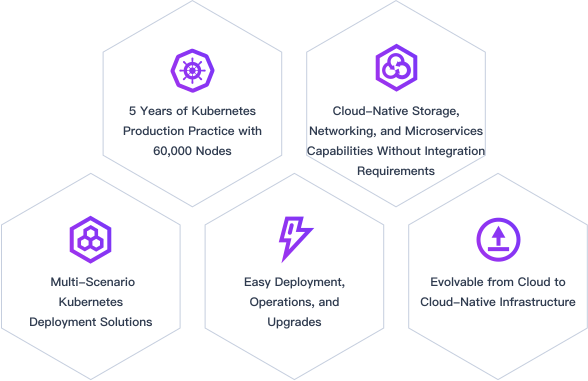
Why EasyStack Cloud-Native Foundation (ECNF)?
EasyStack Cloud Native Foundation (ECNF) integrates infrastructure, cloud-native technologies, and management into a unified platform. This platform comprises EKS Kubernetes clusters, secure containers, runC runtime, secure sandbox (rune) runtime, as well as storage, networking, operating systems, and related components designed for cloud-native applications, all embedded within a digital native engine. With flexible deployment options and an evolvable architecture, it supports the development and operational requirements of modern applications across various infrastructure scenarios.
Integrating Secure Container Service with Cloud-Native Storage and Networking in a Unified Secure Framework
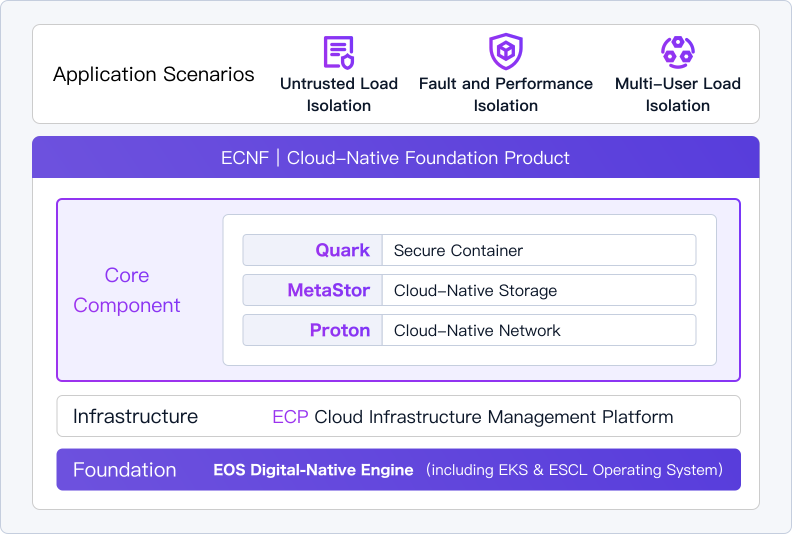
Cloud Storage and Cloud Networking Designed for Cloud-Native Applications
Proton utilizes the widely adopted Kube-OVN as its core, providing a network model and operational experience consistent with instance、secure container and bare metal.
Native integration with MetaStor Cloud-Native Storage, enabling on-demand deployment and scaling.
The cloud infrastructure management platform encompasses capabilities such as cluster deployment, scaling, upgrades, monitoring, logging, alerting, and multi-cluster management.
Technical Advantages and Customer Value

Strong Resource Performance Isolation
Container instances of different tenants on the same node do not share the kernel. In the event of a kernel or runtime vulnerability, malicious code cannot attack other applications and system services or steal data. Users with host machine permissions cannot view the runtime status of containers, including executing command lines or accessing all application runtime-related information.

Highly Compatible
Complies with the OCI container implementation specifications and uses Kubernetes standard RuntimeClass for seamless integration with Kubernetes. There is no need for additional processing of container images, and applications running on runC containers can run directly on secure containers without modification.

High Maturity
The secure sandbox (rune) runtime utilizes Kata Containers technology, which has gained widespread support in the industry. It boasts a robust and active open-source community and has been successfully deployed on a large scale in several financial institutions and internet companies.

Security and Compliance
Whether deployed in public clouds, private clouds, or physical machines, system must implement strong kernel-level isolation for container instances.
Proton Cloud Load Balancer: Facilitating Efficient Coordination in Container Environments

Proton Cloud Load Balancer
In a containerized environment, the use of a software load balancer (ELB) offers multiple advantages. First, it simplifies the process of external access to container workloads by enabling seamless integration with ELB through associated Ingress, thereby enhancing overall efficiency by allowing direct access to container workloads. In disaster recovery scenarios, the ELB acts as the traffic entry point, ensuring even distribution of traffic across multiple container instances, which further enhances system stability. Additionally, it meets the isolation requirements of project teams by providing each team with a dedicated load balancer, allowing for independent configuration and management of resources.
In container scenarios, Pod resources can change dynamically. Software load balancing can more easily adapt to these changes, such as supporting automatic failover for ingress-controller pods and on-demand scaling. These requirements are challenging to meet with hardware load balancers in cloud-native applications.
In container scenarios, independent load balancing instances can be allocated based on project team dimensions, allowing exclusive access to CPU, memory, network, and other resources. This approach meets the load balancing requirements of various business scenarios.
Flexible configuration of active-active instances provides robust reliability and high availability. Withstanding peak loads and avoiding bottlenecks, the high-performance load balancing achieved through active-active topology supports up to 500,000 QPS per instance, effortlessly handling tens of thousands of concurrent requests and enabling rapid responses to market changes.
Flexibly control the load balancer by enabling or disabling listeners, resource pools, and members to achieve precise traffic control. It intelligently distributes traffic requests and supports various load balancing algorithms to optimize the utilization of backend service resources. With support for multiple protocols, it adapts to various scenario requirements, creating personalized load balancing services.
Proton LB supports four-layer load balancing for TCP, UDP, and PROXY protocols, helping network applications achieve high performance and high availability. It also offers seven-layer load balancing for HTTP and HTTPS protocols, intelligently distributing requests and comprehensively covering your application services.
Flexible Deployment Models Enable Seamless and Agile Cloud-Native Migration